JANMEJAYA
SWAIN
Building Secure Systems. Protecting Global Scale. Specializing in Application Security, Secure Architecture and AI Security.
Recognised by global leaders in tech & finance
6+
Years Experience
1000+
Security Assessments
400+
Enterprise Applications
1
Published CVE
50+
Hall of Fame Recognitions
10+
Certifications
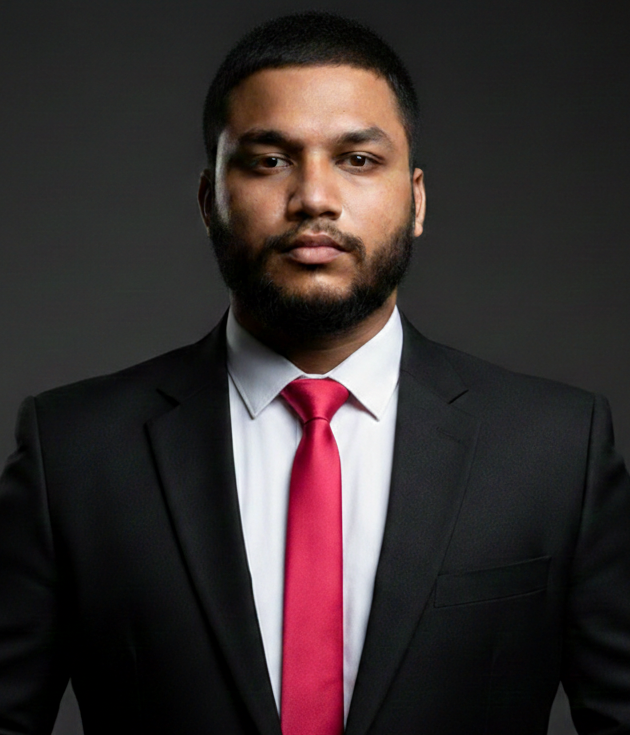
Securing Today. Building a Safer Tomorrow.
Senior Information Security Engineer with over 6+ years of experience helping organizations design secure software, assess complex architectures, and embed security into every stage of the software development lifecycle. My expertise spans Security Architecture, Application Security, Third-Party & SaaS Security Reviews, Security Strategy, AI Security, Secure SDLC, and Offensive Security. As a Dedicated Security Engineer for enterprise programs, I partner with engineering, architecture, and business teams to identify security risks, influence secure design decisions, and strengthen organizational security posture.
Beyond my professional work, I'm an active security researcher, bug bounty hunter, published CVE author, and OWASP Chapter Co-Lead. I'm passionate about advancing cybersecurity through vulnerability research, AI-driven security innovation, security automation, and community knowledge sharing. My mission is to make security an enabler of innovation rather than a barrier to it.
Mastercard
Senior Information Security Engineer
Mastercard
Senior Vulnerability Analyst
PwC India
Cyber Security Consultant
PwC India
Senior Cyber Security Analyst
PwC India
Cyber Security Intern
Kyrion Technologies
Cyber Security Intern
CISM
ISACA
AWS Security
Amazon
CEH
EC-Council
eWPTX v2
eLearnSecurity
eMAPT
eLearnSecurity
AI/ML Pentester
Specialty
Agentic AI
Specialty
PentraxAI
LIVE · Phase 2OPEN SOURCEThe World's First Open-Source LLM-Native Penetration Testing Platform
> Initializing PentraxAI agent...
Scanning attack surface...
[!] SQLi detected — verifying...
[CRITICAL] RCE confirmed · CVSS 10.0
✓ Exploitation verified. No false positive.
Findings: 3 Critical, 5 High, 12 Medium
Cost: $0.73 · False Positives: 0
Why PentraxAI
~Zero False Positives
Every finding actively exploited & verified before hitting your report. No ghost hunting.
$30 Full Pentest Cost
Eliminates $15K+ manual costs. Run deep pentests for the cost of LLM API tokens.
190+ Vulnerability Types
Pure LLM reasoning, zero CVE database dependency. Cognitive analysis of your unique attack surface.
Complete Live Transparency
Watch the AI think. See every payload, every response, and every logical pivot in real time.
Attack Chain Discovery
Agents connect low-severity findings into critical exploitation paths — just like human red teams.
Open Source · MIT License
Self-hostable. Community-driven. No black boxes, no vendor lock-in. Full transparency.
Roadmap
Core LLM-native reasoning engine designed. Multi-agent attack orchestration validated. Zero false-positive methodology established.
PentraxAI is live in PoC stage — actively tested against real targets in controlled environments. Results validated by security researchers.
Ongoing Project
Built in the Open. For Everyone.
MIT Licensed · Self-Hostable · Community Driven · Full Transparency
+ and many more...
- Many more Private Programs
Names confidential
- Microsoft
- X (formerly Twitter)
- CoinBase
- Apple
- Google (5+ times)
- SAP
- Paytm (7+ times)
- Synology
- Blackberry
- Springer Nature
- Skyscanner
- SEEK
- Avira
- United Nations Women
- United Nations
- Inflectra
- Keybank
- NCIIPC – Government of India
- Drexel University
- Bigbank
- University of Oxford (3 times)
- OnePlus
- TIDEPOOL (20+ times)
- NCSC – UK Government
> 7+ years of continuous security research on HackerOne
Chapter Co-Lead
OWASP Bhubaneswar Chapter
- Community Building
- Security Awareness
- Training & Workshops
- Mentoring
Master of Cyber Security
Pursuing
Charles Sturt University, Australia
B.Tech in Computer Science & Engineering
Orissa Engineering College, Bhubaneswar
Let's build a more secure digital world together
Whether you need a security architecture review, penetration testing, or guidance on building secure AI systems, I'm here to help.